
Analyses and publications
Cybersecurity blog
Analyses of attacks, phishing campaigns and malware seen in the field, explanations of the NIS2 legal framework, and notes from conferences and research work.
- Critical PHP vulnerabilities (21 October 2026): what every organisation should do
 Two critical PHP vulnerabilities, scored CVSS 9.2, are patched on 21 October 2026 at 14:00 UTC. The risk is global, not just British: which systems are exposed and what to do before and after patching.
- Ransomware attack: what to do in the first 72 hours to limit losses and preserve evidence
 The first 72 hours after a ransomware attack decide how much a company loses and whether any evidence survives for a criminal case. The concrete steps, in the right order.
- Incident notification under Romania’s NIS2 law: 24 hours, 72 hours, one month
 The incident reporting deadlines in art. 15 of GEO 155/2024, what each stage contains, who qualifies an incident as significant and what to prepare in advance.
- NIS2 in a group of companies: scope is set per entity, and DNSC Decision no. 3/2026
 In a group, NIS2 scope is determined per entity, without aggregating figures. What cannot be centralised, the control matrix, and DNSC Decision no. 3/2026.
- NIS2 maturity self-assessment in Romania: the EVAL_MMS tools, the thresholds and the remediation plan
 How the annual self-assessment under art. 12 (4) works: documentation and implementation scores, thresholds per level, capped N/A exclusions and the remediation plan.
- CyFun and the self-assessment spreadsheet: where the 218 controls in DNSC Order no. 1/2026 come from
 Where to download the CyFun Excel tools, how the two dimensional scoring works, and how it relates to the 218 controls in Romania’s DNSC Order no. 1/2026.
- „NIS2 certification”: what really exists and what is sold under that label
 An organisation cannot be certified NIS2. What art. 24 of the directive covers, what GEO 155/2024 requires instead, and what is actually sold under that label.
- The NIS auditor in Romania: who may audit, the DNSC attestation and the public list
 NIS2 audits in Romania require a DNSC attestation valid for three years. The art. 58 incompatibilities, the public list, and what to ask a provider before signing.
- Analysing a large case file: from thousands of pages to verifiable facts
 How to organise a case file of thousands of pages: inventory, index reconciliation, chronology, person index, metadata analysis and the limits of documentary analysis.
- The NIS officer in Romania: duties, appointment, training and what DNSC does not certify
 What art. 14 of GEO 155/2024 requires, the five conditions for essential entities, which occupational codes are used, and why DNSC does not license NIS officers.
- The DNSC notification form and the NIS2@RO platform: how registration is done correctly
 The only regulated DNSC form is the registration notification. Its six sections, who signs, the three filing channels and the mistakes that keep repeating.
- Apply AI Alliance of the European Commission accepts three ProDefence publications on artificial intelligence
 Three works by Alexandru Angheluș, the study on civilizational transformation, the Humanᴬᴵ and Orgᴬᴵ framework and its calculator, are published on the European Commission’s Apply AI Alliance.
- Romania’s NIS2 law: where to find the official text of GEO 155/2024
 Where to read the free consolidated text of GEO 155/2024 and Law 124/2025, what the 23 amending points changed, and how to cite Romanian NIS2 law.
- US renames artificial intelligence “Super Intelligence”: what changes for organisations in Romania and the EU
 The executive order signed on 29.09.2026 requires US federal agencies to use “Super Intelligence” instead of “Artificial Intelligence”. What it says, why the term is confusing, and why the AI Act, NIS2 and organisations’ documents in the EU do not change.
- Romania’s first NIS2 fine: 50,000 lei for failing to register, not for incidents
 Romania’s first NIS2 penalty is 50,000 lei under art. 60 (1) o) of GEO 155/2024. It concerns the registration notification, not incident reporting.
- DNSC draft: NIS2 training standard for management bodies and the list of 61 certifications
 DNSC is preparing a draft decision setting the cybersecurity training standard for the management bodies of essential and important entities: 6 competence units, assessment through crisis simulation and a governance portfolio, plus the list of 61 recognised certifications. The document is a draft, not an act in force.
- Public administration: 2.07 out of 5 on independent evaluations. DNSC’s blunt conclusion
 DNSC: public institutions do not carry out independent evaluations of their own infrastructure. What CyFun control ID.IM-03.7 and GEO 155/2024 require.
- Digital infrastructure: 4.79 out of 5 on crisis communication. What NIS2 asks beyond a spokesperson
 CyFun control RC.CO-04.2 and the GEO 155/2024 deadlines. Public communication and statutory reporting are two separate flows.
- The HumanAI and OrgAI Calculator: a guided tour
 What you see, what you enter and what you get, screen by screen, through the eight modules and the diagnostic.
- Financial market infrastructure: 4.83 out of 5 on backups. The best DNSC score and what still needs proving
 The highest score in the DNSC series, on CyFun control PR.DS-11.1. What it does not cover and how NIS2 and DORA are delimited.
- Energy: 2.15 out of 5 on the critical supplier register. Supply chain risk under NIS2
 CyFun control GV.SC-07.2 requires a critical supplier list, online and offline. Why it matters in the first hours of an incident.
- HumanAI and OrgAI: what capacity has the organisation built
 The difference between individual AI use and governed organisational capacity is not one of scale but of architecture.
- Postal and courier: 2.00 out of 5, the weakest DNSC score. A sector that does not track its own obligations
 CyFun control GV.OC-03.2 measures how legal obligations are managed. Three GEO 155/2024 deadlines that are missed most often.
- The HumanAI and OrgAI Framework Calculator, version 1.2.0
 A free instrument for assessing AI-mediated capacity. A single HTML file, no installation, no account and no network requests.
- Health: 2.34 out of 5 on management training. The one CyFun control written directly into law
 Art. 14 (2) of GEO 155/2024 requires accredited training for management bodies. What the DNSC score shows for Romania’s health sector.
- Transport: 2.68 out of 5 on data identification. The inventory that blocks NIS2 compliance
 CyFun control ID.AM-07.1 requires data to be identified. Without an inventory there is no risk analysis, continuity plan or 72-hour notification.
- NIS2 officer in Romania: important entities must appoint one too, not only essential entities
 Art. 14 para. (3) of Romania GEO no. 155/2024 requires the appointment of the officer responsible for the security of networks and information systems at both essential and important entities. Para. (4) is not an exemption, it sets the profile criteria for that person in a subset. Text analysis, comparison table and what waiting actually risks.
- Managed ICT services: 2.88 out of 5 on automation. Providers are checked twice under NIS2
 A low DNSC score on CyFun control ID.IM-03.6. Why managed service providers answer both for their own obligations and for their clients’.
- NIS2 implementation in Romania: in-house, with a consultant, or an outsourced NIS2 officer
 In-house, with a consultant, or an outsourced NIS2 officer through CISO as a Service. What each route involves, what it costs and how to choose, under GEO 155/2024.
- Chemical sector: 4.40 out of 5 on web and e-mail filtering. What comes next under NIS2
 DNSC published the chemical sector’s maturity score for CyFun control PR.PS-05.1. What the figure confirms and what GEO 155/2024 requires next.
- CysNIS platform ranked 9th in IT & Tech at INNOVENTURE 2025-2026
 ProDefence’s CysNIS platform ranked 9th in the IT & Tech category at INNOVENTURE 2025-2026 with a score of 3.85. The full ranking and what it means.
- Alexandru Angheluș publishes “Transformation” — AI, human autonomy and the cognitively assisted Earth
 Alexandru Angheluș has published “Transformation”, a work examining artificial intelligence beyond its conventional role as a technological application and analysing it as an emerging cognitive layer positioned between human beings and reality.… Read more: Alexandru Angheluș publishes “Transformation” — AI, human autonomy and the cognitively assisted Earth
- ADA guide released in Romanian and English: AI and the manipulation of human perception
 ProDefence has published the educational guide “Artificial Intelligence and the Manipulation of Human Perception” in both Romanian and English. The guide was developed under the ADA programme: Analyze, Decide, Act, initiated by… Read more: ADA guide released in Romanian and English: AI and the manipulation of human perception
- AI vs phishing: who wins? A test from the ADA campaign
 Published in July 2025 as part of the ADA campaign. The platform announced at the time now operates as CysEdu. Can artificial intelligence recognise a phishing message better than a person? In… Read more: AI vs phishing: who wins? A test from the ADA campaign
- ProDefence at the Regional Conference of Intelligence Analysts: financial fraud and disinformation in the age of AI
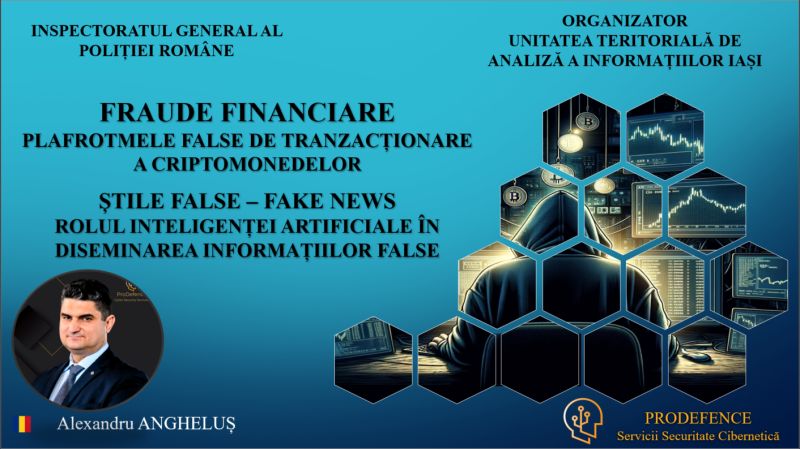 Event report, November 2024. In November 2024, ProDefence CEO Alexandru Angheluș spoke at the Regional Conference of Intelligence Analysts in Iași about fake cryptocurrency trading platforms and the role of artificial intelligence… Read more: ProDefence at the Regional Conference of Intelligence Analysts: financial fraud and disinformation in the age of AI
- ProDefence at the BlackSea Maritime Cybersecurity Conference: investigating cybercrime in a time of conflict
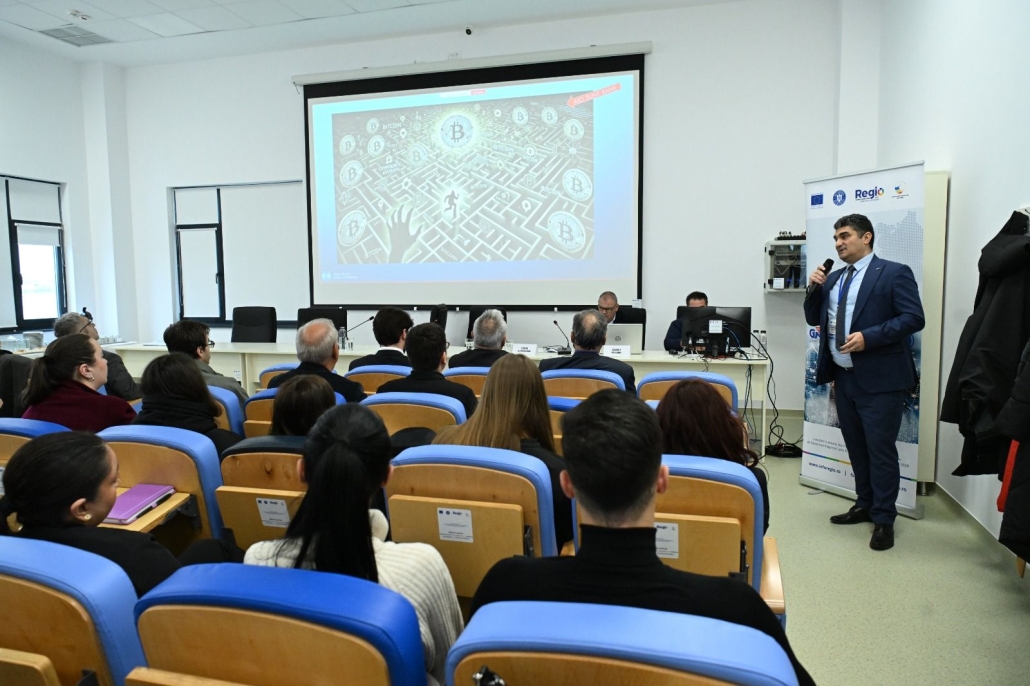 Event report, November 2024. On 21–22 November 2024, the Maritime University of Constanța hosted the first edition of the BlackSea Maritime Cybersecurity conference, themed “Countering cybercrime threats in the current context of… Read more: ProDefence at the BlackSea Maritime Cybersecurity Conference: investigating cybercrime in a time of conflict
- ProDefence CEO contributes to Moldova’s cybersecurity capacity building at an e-Governance Academy workshop
 Event report, November 2024. Alexandru Angheluș, CEO of ProDefence and President of the Cyber Security Cluster of Excellence (CYSCOE), took part as a cybersecurity expert in a workshop organised by the Ministry… Read more: ProDefence CEO contributes to Moldova’s cybersecurity capacity building at an e-Governance Academy workshop
- CYSCOE at the Romanian Tourism Fair: how stealer malware led to fraud at a travel agency
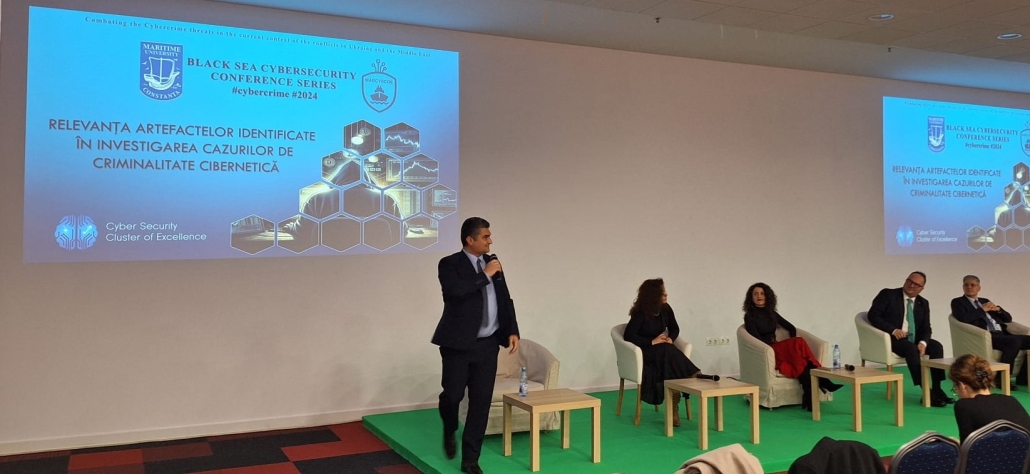 Event report, November 2024. At the Cybersecurity Workshop for Travel Agencies, held during the Romanian Tourism Fair at RomExpo, ProDefence represented the Cyber Security Cluster of Excellence (CYSCOE) with a real case:… Read more: CYSCOE at the Romanian Tourism Fair: how stealer malware led to fraud at a travel agency
- ProDefence at the Bucharest Cybersecurity Conference 2024
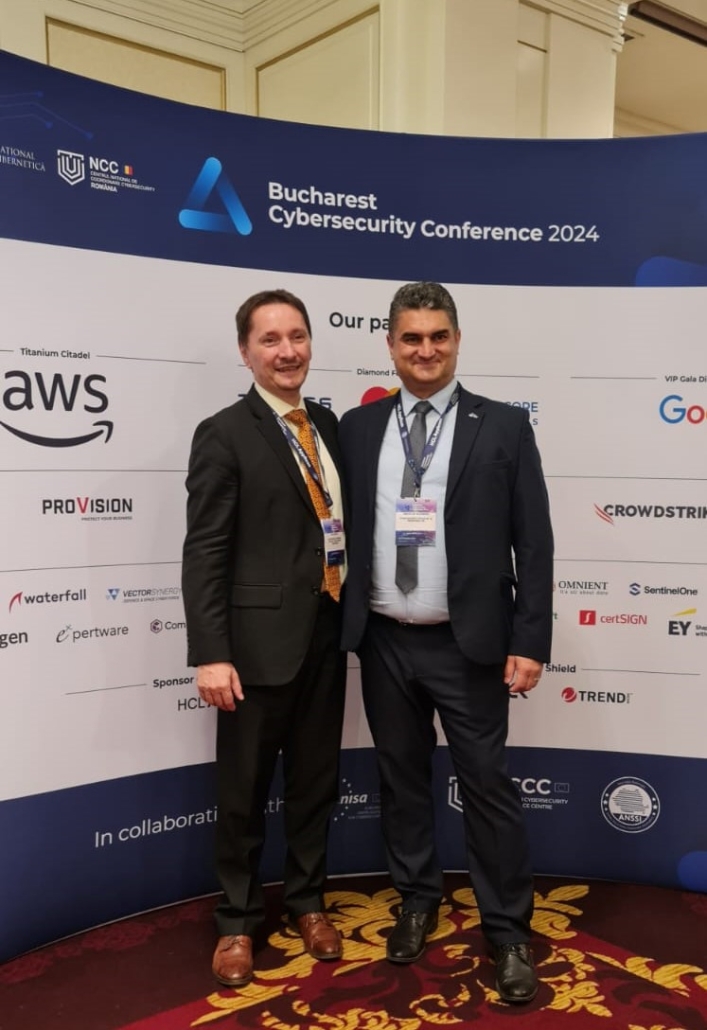 Event report, October 2024. From 29 to 31 October 2024, ProDefence CEO Alexandru Angheluș, also President of CYSCOE, took part in the Bucharest Cybersecurity Conference 2024, which brought together government, industry and… Read more: ProDefence at the Bucharest Cybersecurity Conference 2024
- CYSCOE and Iași Police: joint call for cyber awareness
 Event report, September 2024. Alexandru Angheluș, President of the Cyber Security Cluster of Excellence (CYSCOE) and CEO of ProDefence, joined Chief Police Inspector Florin Ionuț Zaborilă, head of the Cybercrime Investigation Unit… Read more: CYSCOE and Iași Police: joint call for cyber awareness