Event report, October 2024.

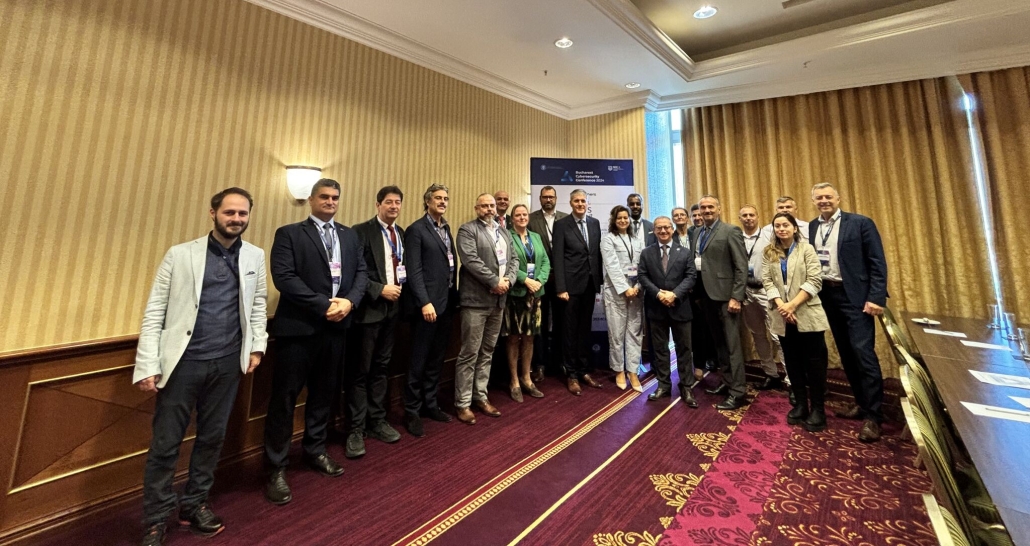
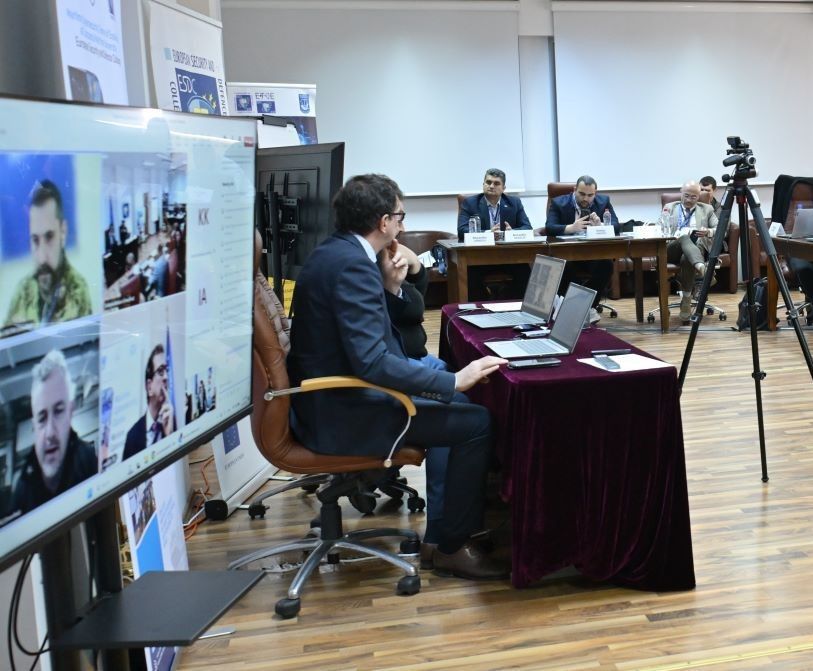
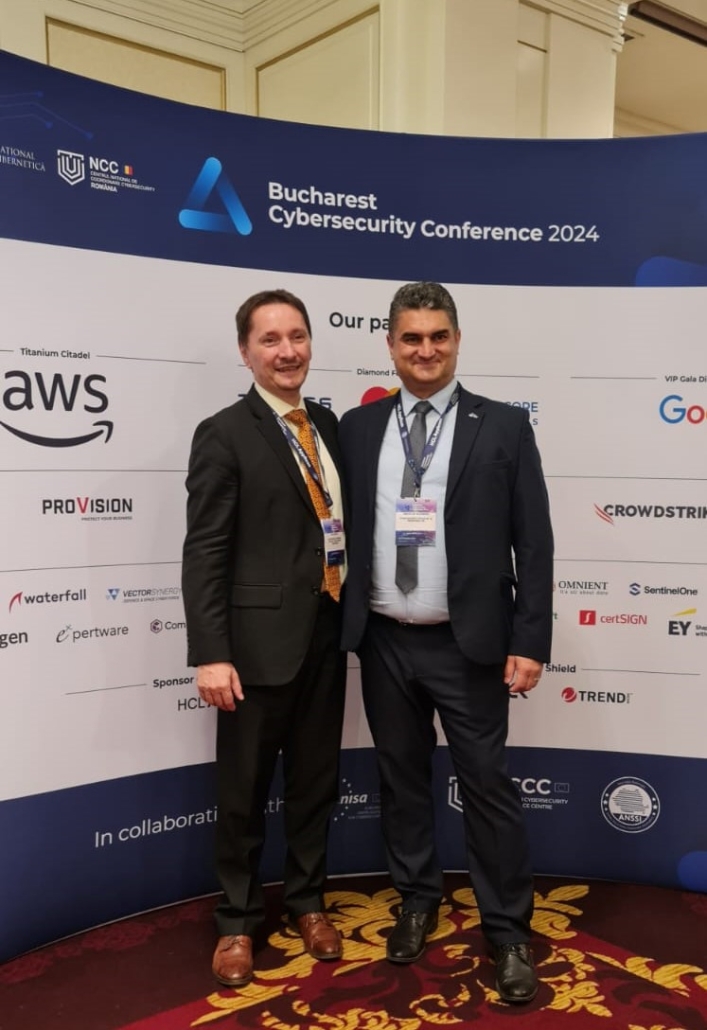
From 29 to 31 October 2024, ProDefence CEO Alexandru Angheluș, also President of CYSCOE, took part in the Bucharest Cybersecurity Conference 2024, which brought together government, industry and academia. He contributed to the DNSC Cybersecurity Conference and the ENISA “Cybersecurity Resilience & Market” Forum, on topics ranging from coordinated vulnerability disclosure to NIS2 and the EU Cyber Resilience Act.

Key points

  • Coordinated vulnerability disclosure (CVD) policy in Romania was one of the main topics.
  • Critical sectors such as maritime and healthcare need specific resilience and risk management measures.
  • National strategies must align with NIS2, the Cyber Resilience Act and other European frameworks.
  • Public-private partnerships and skills development were recurring themes.

Themes discussed

  • implementing a coordinated vulnerability disclosure (CVD) policy in Romania;
  • strengthening cyber resilience in critical infrastructure, including maritime and healthcare;
  • cyber risk management in maritime operations;
  • threats and vulnerabilities in the healthcare sector in a changing threat landscape;
  • aligning national strategies with NIS2, the EU Cyber Resilience Act and other European frameworks.

Alexandru Angheluș joined discussions alongside Dan Cimpean, Director of the National Cyber Security Directorate (DNSC).

Collaboration at the core

The conference worked as a catalyst for public-private partnerships and cross-sector coordination. The roundtables stressed the need for skills development, policy innovation and strategic alignment to protect Europe’s digital infrastructure at a time of growing geopolitical and technological risk.

“At BCC 2024, we explored essential cybersecurity priorities with impact across industries. As ProDefence and CYSCOE, we remain committed to shaping a safer, more resilient digital Europe.” (Alexandru Angheluș)

Acknowledgements

ProDefence congratulates the DNSC team and all partners for an event that exceeded expectations in scope and substance. Special thanks to Dan Cimpean, Sebastian Dan, Mirabela Săvulescu, Aurel Huștea, Fraga Tariuc, Gabriel Dinu, Mihaela Curcă and the whole organising team.

Related

ProDefence applies these priorities in practice through NIS2 compliance consulting, the outsourced NIS2 officer service and its own responsible disclosure policy. The full Romanian legal framework is summarised on NIS2 Directive in Romania.

Event report, September 2024.

Alexandru Angheluș, President of the Cyber Security Cluster of Excellence (CYSCOE) and CEO of ProDefence, joined Chief Police Inspector Florin Ionuț Zaborilă, head of the Cybercrime Investigation Unit of the Iași County Police Inspectorate, in a press conference on the growing wave of online fraud affecting Romanian citizens. The message: most attacks start with manipulation, and a short pause to verify prevents most losses.

Key points

  • Phishing remains the main entry point for online fraud.
  • “Money recovery” schemes target people who have already been defrauded.
  • Social engineering exploits trust and low digital literacy.
  • Two-factor authentication and verification before acting stop most attacks.

Threats discussed

Online fraud and phishing

Criminals use messages that look legitimate to trick people into giving away personal and financial data.

“Money recovery” fraud

An emerging tactic: victims are promised help to recover lost money, then fall into a second scam run by the same or affiliated criminals. Legitimate institutions do not ask victims for fees to recover funds.

Social engineering

Attackers manipulate trust, urgency and lack of digital experience to break into accounts and systems.

Advice for citizens

  • enable two-factor authentication on email, banking and social media accounts;
  • pause and verify before clicking, paying or sharing data;
  • treat cyber education as a form of prevention;
  • follow alerts from the National Cyber Security Directorate (DNSC) and contact DNSC when you notice suspicious activity;
  • use the resources published by ProDefence and Cyber AID on recognising fraud and phishing.

Public-private collaboration

Alexandru Angheluș stressed that cooperation between public institutions and the private sector is essential against cybercrime: only joint action builds a digital space that is secure, resilient and trusted. CYSCOE thanks the institutions involved and TVR Iași for spreading the message.

Full interview and footage: youtu.be/PO4k1iqoCmI.

If you have been defrauded

Report the case to the police and to your bank immediately. For documenting what happened, ProDefence offers analysis of electronic fraud and suspicious files and support in cybercrime cases.

Financial fraud and digital disinformation are two deeply interconnected phenomena, which have evolved, in the last two decades, from opportunistic, marginal practices into real criminal industries with a global impact. They erode trust in financial markets, destabilize economic and political institutions, and weaken social cohesion and democracy itself, by manipulating the masses and exploiting people’s cognitive vulnerabilities.

Essentially, financial fraud aims to obtain illicit gains by misleading victims, and disinformation serves as a multiplier of this effect, creating false narratives, legitimizing scams, and neutralizing warnings from authorities. The two naturally converge: for a fraud to succeed on a large scale, it needs an information framework to support it — and for disinformation to have an economic effect, it must be directed towards false financial opportunities.

In this context, the emergence and democratization of artificial intelligence (AI) tools has fundamentally changed the dynamics of these risks. On the one hand, AI has made it cheaper, faster, and more sophisticated to produce scams, deepfakes, and fake news — lowering the barrier to entry for malicious actors and increasing the effectiveness of their campaigns. On the other hand, the same technology has provided organizations and authorities with better defense tools: from systems for automatic detection of financial anomalies and suspicious behavior, to tools for analyzing networks and dismantling disinformation campaigns.

Today, attackers and defenders operate on the same technological terrain, in an ever-accelerating competition. Artificial intelligence has thus become a multiplier of human intent, capable of amplifying both risks and responsiveness.

This article aims to explore this complex and dual landscape: how fake cryptocurrency platforms are used to defraud users, how they rely on disinformation to ensure their success, and how artificial intelligence serves as both an accelerator of these threats and an essential countering tool. We will look at the mechanisms used by criminals, the impact on public trust, as well as best practices and emerging technologies in defending against this phenomenon.

Fake cryptocurrency platforms: financial fraud in the digital age

In the digital age, cryptocurrencies have simultaneously become a symbol of financial innovation and an opportunity for crime. The popularity of Bitcoin, Ethereum, and other digital assets has attracted millions of investors, as well as criminal groups that exploit a lack of financial literacy and insufficient regulation. Among the most prevalent methods are fake crypto trading platforms, which are elaborate, persuasive, and difficult to expose.

How do these platforms work?

Attackers use a combination of social engineering, technology, and behavioral psychology to create seemingly legitimate platforms. Typical features:

  • Professional design and fictitious legal details: sites with interfaces identical to those of established platforms, complete with copied legal terms, valid SSL certificates and convincing branding elements.
  • Trap domains: The use of domains that differ from the original ones by a character or extension (e.g., “.co” instead of “.com”).
  • Intense promotion: Social media ads, investment forums, unsolicited emails, all supported by auto-generated fake reviews.
  • AI-powered chatbots: to answer victims’ questions in real-time, reinforcing the appearance of legitimacy.

Why does it work?

These schemes succeed because they exploit:

  • people’s desire for quick gain (FOMO – fear of missing out);
  • excessive reliance on visual and testimonial appearances;
  • the real complexity of the crypto market, which makes it difficult to assess opportunities.

Impact:

  • Individual losses ranging from a few hundred to hundreds of thousands of dollars.
  • Destruction of the victims’ life savings.
  • Reputational losses for the legitimate crypto industry.
  • Contributing to global money laundering flows and financing other criminal activities.

Digital Disinformation: The Catalyst for Scams

Financial fraud at scale cannot exist without an information ecosystem to validate it. Disinformation plays this essential role, creating the ‘narrative’ that lends credibility to fraudulent platforms and blocks warning messages from authorities.

Common disinformation tactics:

  • Content blizzard: the massive publication of thousands of posts, fake news, reviews, which flood the information space, making it difficult to identify the truth.
  • Deepfakes: the use of images/videos of personalities that apparently promote the platform, to confer legitimacy.
  • Coordinated campaigns: thousands of automated social media accounts that repeat the same narrative, generating the perception of a majority.
  • Discrediting warnings: spreading conspiracy theories to weaken trust in regulators.

Consequences:

  • Emotional manipulation of victims.
  • Creating a climate of confusion and mistrust.
  • Weakening the effectiveness of the authorities’ response.

The Carnegie Endowment points out that these campaigns are rarely strictly financial: they often also serve political or geopolitical purposes, using the same arsenal.

AI role: Double-edged sword

Artificial intelligence has established itself as a decisive factor in the fight between attackers and defenders, becoming a multiplier of efficiency for both sides. The same technologies that can be used to detect fraud and disinformation are also easily used to produce them on a large scale and with a high degree of sophistication.

In the hands of the attackers

Attackers quickly adopted AI, exploiting its accessibility and power to expand their operations and mask their intentions. Among the most relevant uses are:

Content generation at scale

  • Language algorithms (such as LLMs) automatically produce texts, articles, reviews, and messages that appear genuine. They are tailored to the target audience, with specific tone and vocabulary, so as to increase the credibility of fake platforms.
  • Huge volumes of content can be generated in a matter of minutes, filling the information space with false narratives and covering legitimate messages.

Extreme customization

Using data collected from social media, data leaks, and OSINT, attackers personalize phishing messages according to each victim’s preferences, habits, and vulnerabilities.

  • An AI-generated email can include personal details that make it seem believable and hard to distinguish from genuine communication.
  • This hyper-personalization significantly increases the success rate of attacks.

Interaction automation

Intelligent chatbots, trained on specific scenarios, can respond to victims on fake platforms 24/7.

  • Chatbots can have complex conversations, answering questions, assuaging doubts, and convincing the victim that the platform is genuine.
  • This reduces the need for human personnel and increases the scalability of the operation.

Deepfakes

Image and video generation technologies are used to create materials in which public figures, executives or specialists appear (falsely) promoting the fraudulent platform.

  • During video calls or online conferences, deepfakes can convince victims that they are talking to someone they trust.
  • These materials increase the emotional pressure and credibility of the scheme.

In the hands of the defenders

On the other hand, AI also provides defenders with powerful tools to detect and counter attacks. Key uses include:

Anomaly detection

Specialized algorithms can analyze millions of transactions or interactions in real-time to identify unusual patterns.

  • They can flag suspicious activity, such as repetitive transactions, logins from unusual locations, or behaviors that don’t fit the user’s regular profile.
  • These systems are fundamental to protecting banks, exchanges, and exchanges.

Automatic content classification

Machine learning-based classification systems analyze text, images, and videos to assess the likelihood that they are false or misleading.

  • They can filter reviews, comments, and news in real-time, reducing the spread of misinformation.
  • They are used by social platforms, news agencies, and regulators.

Network analysis

AI enables mapping and analyzing relationships between thousands or millions of accounts, sites, and transactions.

  • By graphically analyzing these connections, investigators can identify key nodes and dismantle coordinated campaigns.
  • This technique is used in investigations into botnets, troll farms and money laundering networks.

Media Verification

AI tools that specialize in “media forensics” can analyze metadata, visual inconsistencies, and sound patterns to determine if an image or video has been manipulated. They can recognize deepfakes and artificially generated content, helping to protect public opinion and institutions from manipulation.

Artificial intelligence is undoubtedly a double-edged sword. In the hands of criminals, it can produce more convincing, cheaper, and harder-to-detect scams. In the hands of defenders, however, AI is becoming an indispensable ally, providing the ability to analyze data at scale, detect anomalies, and respond quickly to threats.

The success of the fight against fraud and disinformation depends not only on technology, but also on who uses it more effectively.

Recommendations

For users:

Although attackers are using increasingly sophisticated technologies, users can greatly reduce the risk of becoming victims through a combination of caution, information, and basic cybersecurity practices. Here’s how the most important measures can be applied correctly:

Always check the authenticity of platforms and URLs

  • Before investing money or entering personal data, carefully examine the site’s address.
  • Make sure that the domain is spelled correctly, with no extra or suspicious characters (e.g., “binancee.com” instead of “binance.com”).
  • Check for SSL certificates (the padlock icon in your browser), but keep in mind that this doesn’t guarantee legitimacy — only connection security.
  • Search the platform in the official lists of financial regulators (ex. ASF, SEC, FCA, etc.) to see if it is authorized.

Avoid decisions under emotional pressure

  • Attackers intentionally create a sense of urgency (offer valid “only today”, limited slots, timers), to prevent rational analysis.
  • Take a break, seek the advice of a friend or specialist and do not give in to the impulse.
  • Remember: Real investments don’t require instant decisions, and legitimate opportunities don’t disappear overnight.

Use multi-factor authentication and anti-phishing extensions‑

  • Enable multi-factor authentication (MFA) wherever possible — preferably with an authenticator app (Google Authenticator, Authy), not via SMS.
  • MFA adds an extra layer of protection, making it more difficult for attackers to gain access even if the password is compromised.
  • Install anti-phishing‑and website reputation check extensions (e.g. Netcraft, Malwarebytes Browser Guard, Bitdefender TrafficLight) to be alerted in case of sites known to be fraudulent.

Search for information from official sources

  • Before investing or filling in personal data, document from credible sources: government websites, regulatory authorities, recognized specialized publications.
  • Avoid relying solely on reviews or forums — they can be manipulated through disinformation campaigns.
  • Check the news about the platform in multiple independent sources and be skeptical of “too good to be true” promises.

These simple but essential practices can protect your savings and give you time to analyze situations with lucidity. In the face of increasingly sophisticated schemes, educated and vigilant users are the first line of defense against financial fraud and disinformation.

For organizations:

Organizations — be they financial institutions, technology companies, crypto platforms or online service providers — are frequent targets of attacks and at the same time vectors through which fraud or disinformation can spread. They bear the responsibility to protect their users, data, and reputation. Implementing proactive measures is essential to prevent incidents or limit their impact.

Deploy AI technologies for monitoring and detection

  • Artificial intelligence and machine learning algorithms are indispensable for analyzing the huge volumes of data generated by transactions and interactions.
  • They can detect anomalies, suspicious behavior, or coordinated campaigns before they cause significant damage.
  • Examples: detecting transactions with typical characteristics of money laundering, recognizing phishing attempts by analyzing the content of emails or identifying fake accounts on social networks.
  • It is essential that the models are constantly updated to keep up with the evolution of attack tactics.

Educate employees about emerging tactics

  • Employees are often the weakest link in the security chain, and attackers exploit this reality through phishing, social engineering, and deepfakes.
  • Organisations must invest in continuous training programmes, which include:
  • recognition of fraudulent messages and websites;
  • awareness of the risks related to data sharing;
  • Periodic phishing simulations to test the vigilance of the teams.
  • Education should be tailored to roles and levels of responsibility, not delivered generically.

Collaborate with authorities and other industry players

  • Cyber threats are rarely isolated — they are global and distributed.
  • Organizations must actively participate in the exchange of information within  threat intelligence sharing communities, together with authorities, competitors and other relevant entities.
  • Examples of such collaborations include participation in incident response centres (CSIRTs/CERTs), public-private partnerships or sectoral working groups.
  • The rapid exchange of indicators of compromise (IoCs), tactics, techniques, and procedures (TTPs) enables faster and more effective responses to threats.

Develop clear incident response protocols

  • No matter how robust prevention is, no system is infallible. It is vital that organizations have well-defined response plans, tested and known by the teams.
  • An incident response plan should include:
  • rapid identification and containment of the threat;
  • internal and external notification (including to authorities and customers, where applicable);
  • remedial and recovery procedures;
  • post-incident review to identify lessons learned.
  • Periodic incident simulations (tabletop exercises) help maintain the organization’s readiness.

Organizations are not only potential victims, but also part of the defense ecosystem against fraud and disinformation. Success in protecting them and their users depends on:

  • adoption of appropriate technologies;
  • continuous training of staff;
  • cooperation with relevant partners;
  • clear and tested plans for crisis situations.

Investing in these measures not only reduces risk, but also protects customer reputation and trust — critical assets in any industry.

For authorities:

National and international authorities — governments, regulators, law enforcement agencies and multilateral institutions — have a crucial role to play in setting the framework within which both financial innovation and protection against abuse take place. As financial fraud and disinformation are amplified by artificial intelligence, authorities need to adopt proactive, pragmatic and well-calibrated measures.

Develop policies adapted to new technologies

  • Traditional regulations are often overtaken by the pace at which technology evolves.
  • It is essential that authorities create policies and regulations that:
  • they take into account the specifics of blockchain, cryptocurrency, AI and deepfake technologies;
  • establish clear responsibilities for platforms and providers;
  • protect consumers without stifling innovation. A clear but flexible framework helps the market to develop safely and prevents systematic abuses.

Invest in AI Defense Tools

  • Just as criminals use AI to attack, authorities must use the same technologies to defend themselves.
  • It is necessary to finance the development and implementation of:
  • automated fraud and disinformation monitoring systems;
  • network analysis algorithms for detecting coordinated campaigns;
  • forensic tools capable of identifying deepfakes and manipulated content. Investing in strengthened AI infrastructure reduces response time and increases the efficiency of investigations.

Encourage public-private partnerships and information sharing

  • No actor, whether governmental or private, can combat these threats alone.
  • It is vital to encourage cooperation between:
  • regulators, police and intelligence services;
  • financial institutions, technology platforms and research organisations;
  • international partners and regional alliances. The rapid exchange of indicators of compromise (IoCs), emerging tactics, and statistical data helps prevent attacks at an early stage and reduce their impact.

Financial fraud and disinformation are fueled by the same raw material: people’s trust and emotions. Artificial intelligence has exponentially amplified both the power of these threats and the ability to counter them.

Effective response requires:

  • Constantly adapted technology to keep up with attackers.
  • Continuous digital education, to raise the level of awareness and competence of citizens and professionals.
  • International collaboration across sectors, as threats do not respect national borders.

AI is neither good nor bad by nature — just a multiplier of human intent. In the right hands, it can become the most powerful weapon in the defense of truth and financial security.

Introduction

The growing dependence on digital infrastructure in various sectors has exponentially increased the risk of cyber threats. These threats can lead to catastrophic consequences if not properly managed, especially in essential services. Cyber-attacks can disrupt critical operations, compromise sensitive data and cause financial and reputational damage. The NIS 2 Directive seeks to address these risks by mandating robust cybersecurity measures in critical sectors.

Essential services such as energy, transport, banking and healthcare are the backbone of modern society. Disruption can have far-reaching consequences, affecting not only the immediate sector, but also the economy and public safety. As cyber threats become more sophisticated, it is crucial to implement comprehensive cyber security strategies to protect these services from potential attacks.

This paper aims to highlight the importance of implementing these measures by examining potential threats and their impact on essential services. By understanding the risks and the necessary cybersecurity measures, we can better protect critical infrastructure and ensure the continuity of essential services.

Overview of the NIS 2 Directive

The Networks and Information Systems (NIS) 2 Directive is a key piece of EU legislation designed to improve the cyber security of critical infrastructure. It extends the scope of the original NIS Directive, increasing the obligations for Member States and operators of essential services to enhance their cybersecurity capabilities.

Key objectives of the NIS 2 Directive

  • Strengthening cyber security: Improving the security of networks and information systems across the EU.
  • Increased cooperation: Improved cooperation between Member States and the European Union Cyber Security Agency (ENISA).
  • Harmonization of regulations: Ensure consistent cybersecurity requirements across Member States.
  • Improve incident reporting: Establish mandatory reporting of significant cyber incidents to relevant authorities.

Key provisions

  • Broad scope: Includes additional sectors such as health, digital infrastructure and space.
  • Risk management: requires operators to adopt risk management practices, including technical and organizational measures.
  • Incident Response: Mandates the development and implementation of incident response plans.
  • Supply chain security: emphasizes the need to address cyber security risks in the supply chain.

Key services and potential cyber threats

  • Energy
  • Transportation
  • Banks
  • Financial market infrastructures
  • Health sector
  • Drinking water supply and distribution
  • Digital infrastructure
  • Public administration
  • Spazio

Banks

Description:

Banking involves financial institutions offering services such as deposits, loans and foreign exchange. It is essential for economic stability and personal financial security.

Potential Cyber Threats:

  1. Banking System Outages:
    • Description: Cyber attacks can disable banking systems, preventing transactions and access to funds, causing widespread financial disruption.
    • Impact: It affects both individuals and businesses, causing significant economic losses and loss of confidence in financial systems.
    • Examples: DDoS attacks targeting banking infrastructure, such as attacks on several banks in Europe in 2012.
  2. Fraudulent transactions:
    • Description.
    • Impact: Leads to direct loss of money and can cause major reputational damage for financial institutions.
    • Examples: phishing attacks and malware that compromise customers’ bank accounts, such as the Carbanak incident, which stole more than $1 billion from banks around the world.
  3. Customer data security breaches:
    • Description: Security breaches affecting customer data can lead to identity theft and financial fraud, undermining trust in financial institutions.
    • Impact: It affects millions of customers, leading to financial losses and potential lawsuits against banks.
    • Examples: major security breaches such as the Equifax incident in 2017, which exposed the personal data of 147 million people.
  4. ATM network compromise:
    • Description: Attacks on ATM networks can lead to unauthorized cash withdrawals and service interruptions.
    • Impact: It causes financial losses for banks and customers and can create panic among ATM users.
    • Examples: attacks on ATM networks, such as the Jackpotting attack, where ATMs were manipulated to release money in an unauthorized way.

Mitigation Strategies:

  • Real-Time Monitoring and Response: deploy advanced monitoring systems for rapid threat detection and response.
  • Data Encryption: using advanced encryption to protect sensitive customer and transaction data.
  • Multi-Factor Authentication: Implement multi-factor authentication to ensure secure access to bank accounts.
  • Customer Education: Educate customers on recognizing and avoiding phishing attempts and other social engineering methods.
  • Collaboration and information sharing: Promote collaboration between banks and law enforcement agencies to share threat intelligence and best practices.
  • Incident Response Planning: Develop and regularly update incident response plans to ensure rapid and effective responses to cyber incidents.

By understanding these potential threats and implementing robust mitigation strategies, the banking sector can increase resilience against cyber-attacks and ensure the continued provision of essential services.


Introduction

The growing dependence on digital infrastructure in various sectors has exponentially increased the risk of cyber threats. These threats can lead to catastrophic consequences if not properly managed, especially in essential services. Cyber-attacks can disrupt critical operations, compromise sensitive data and cause financial and reputational damage. The NIS 2 Directive seeks to address these risks by mandating robust cybersecurity measures in critical sectors.

Essential services such as energy, transport, banking and healthcare are the backbone of modern society. Disruption can have far-reaching consequences, affecting not only the immediate sector, but also the economy and public safety. As cyber threats become more sophisticated, it is crucial to implement comprehensive cyber security strategies to protect these services from potential attacks.

This paper aims to highlight the importance of implementing these measures by examining potential threats and their impact on essential services. By understanding the risks and the necessary cybersecurity measures, we can better protect critical infrastructure and ensure the continuity of essential services.

Overview of the NIS 2 Directive

The Networks and Information Systems (NIS) 2 Directive is a key piece of EU legislation designed to improve the cyber security of critical infrastructure. It extends the scope of the original NIS Directive, increasing the obligations for Member States and operators of essential services to enhance their cybersecurity capabilities.

Key objectives of the NIS 2 Directive

  • Strengthening cyber security: Improving the security of networks and information systems across the EU.
  • Increased cooperation: Improved cooperation between Member States and the European Union Cyber Security Agency (ENISA).
  • Harmonization of regulations: Ensure consistent cybersecurity requirements across Member States.
  • Improve incident reporting: Establish mandatory reporting of significant cyber incidents to relevant authorities.

Key provisions

  • Broad scope: Includes additional sectors such as health, digital infrastructure and space.
  • Risk management: requires operators to adopt risk management practices, including technical and organizational measures.
  • Incident Response: Mandates the development and implementation of incident response plans.
  • Supply chain security: emphasizes the need to address cyber security risks in the supply chain.

Key services and potential cyber threats

  • Energy
  • Transportation
  • Banks
  • Financial market infrastructures
  • Health sector
  • Drinking water supply and distribution
  • Digital infrastructure
  • Public administration
  • Spazio

Transportation

Description:

The transportation sector involves moving people and goods by air, rail, road and sea. It includes systems such as air traffic control, rail signaling and maritime navigation.

Potential Cyber Threats:

  1. Air Traffic Control Disruption:
    • Description.
    • Impact: It affects passenger safety, causes economic losses for airlines and can lead to chaos at airports.
    • Examples: Distributed Denial of Service (DDoS) attacks on air traffic control systems, such as the FAA incident in the US in 2015.
  2. Failures of Rail Signaling Systems:
    • Description: Hacking signaling systems can cause train collisions and derailments, resulting in significant loss of life and property.
    • Impact: Major risk to passenger and staff safety, economic losses and disruption to rail transport.
    • Examples: attacks on railway signaling systems, such as the cyber attack on Polish railways in 2022.
  3. Compromising Maritime Navigation Systems:
    • Description: Compromised navigation systems can lead to ship collisions or groundings, disrupting global supply chains.
    • Impact: Affects international trade, can cause oil spills and other environmental incidents, and endangers the lives of crews.
    • Examples: cyber attacks on ships’ GPS systems, such as incidents reported in the Strait of Hormuz.
  4. Hacking Public Transportation Systems:
    • Description: Attacks on public transportation systems can disrupt services and pose risks to passenger safety.
    • Impact: It causes delays and cancellations, affects the daily mobility of thousands of people and can create panic among the public.
    • Examples: ransomware attacks on ticketing or subway train control systems, such as the San Francisco Muni incident in 2016.

Mitigation Strategies:

  • Monitoring and Response Systems: deployment of advanced monitoring systems for real-time threat detection and response.
  • Security Audits and Penetration Tests: Conduct regular security audits and penetration tests to identify and remediate vulnerabilities.
  • Incident Response Planning: Develop and regularly update incident response plans to ensure rapid and effective responses to cyber incidents.
  • Collaboration and Information Sharing: Promote collaboration between carriers and government agencies to share threat intelligence and best practices.
  • Critical Infrastructure Protection: Strengthening critical infrastructure protection measures such as access control and encryption of communications.

By understanding these potential threats and implementing robust mitigation strategies, the transportation sector can increase resilience against cyber-attacks and ensure the continued provision of essential services.


Introduction

The growing dependence on digital infrastructure in various sectors has exponentially increased the risk of cyber threats. These threats can lead to catastrophic consequences if not properly managed, especially in essential services. Cyber-attacks can disrupt critical operations, compromise sensitive data and cause financial and reputational damage. The NIS 2 Directive seeks to address these risks by mandating robust cybersecurity measures in critical sectors.

Essential services such as energy, transport, banking and healthcare are the backbone of modern society. Disruption can have far-reaching consequences, affecting not only the immediate sector, but also the economy and public safety. As cyber threats become more sophisticated, it is crucial to implement comprehensive cyber security strategies to protect these services from potential attacks.

This paper aims to highlight the importance of implementing these measures by examining potential threats and their impact on essential services. By understanding the risks and the necessary cybersecurity measures, we can better protect critical infrastructure and ensure the continuity of essential services.

Overview of the NIS 2 Directive

The Networks and Information Systems (NIS) 2 Directive is a key piece of EU legislation designed to improve the cyber security of critical infrastructure. It extends the scope of the original NIS Directive, increasing the obligations for Member States and operators of essential services to enhance their cybersecurity capabilities.

Key objectives of the NIS 2 Directive

  • Strengthening cyber security: Improving the security of networks and information systems across the EU.
  • Increased cooperation: Improved cooperation between Member States and the European Union Cyber Security Agency (ENISA).
  • Harmonization of regulations: Ensure consistent cybersecurity requirements across Member States.
  • Improve incident reporting: Establish mandatory reporting of significant cyber incidents to relevant authorities.

Key provisions

  • Broad scope: Includes additional sectors such as health, digital infrastructure and space.
  • Risk management: requires operators to adopt risk management practices, including technical and organizational measures.
  • Incident Response: Mandates the development and implementation of incident response plans.
  • Supply chain security: emphasizes the need to address cyber security risks in the supply chain.

Key services and potential cyber threats

  • Energy
  • Transportation
  • Banks
  • Financial market infrastructures
  • Health sector
  • Drinking water supply and distribution
  • Digital infrastructure
  • Public administration
  • Spazio

Energy

Description:

The energy sector covers the production, transmission and distribution of electricity, oil and natural gas. It is fundamental to the functioning of all other sectors.

Potential cyber threats:

  1. Grid Outage:
    • Description:Attacks on control systems, such as Supervisory Control and Data Acquisition (SCADA) systems, can cause widespread power outages.
    • Impact: It affects homes, businesses and critical services such as hospitals and emergency response, leading to economic and social chaos.
    • Examples: the 2015 attack on Ukraine’s electricity grid by the Sandworm group, which caused widespread blackouts.
  2. Oil and Gas pipeline disruptions:
    • Description:Cyber intrusions can shut down pipeline operations by targeting industrial control systems (ICS), resulting in significant supply shortages and economic losses.
    • Impact: Disrupts fuel supplies to industries, transportation and homes, causing economic instability and environmental risks.
    • Case in point: the ransomware attack on the Colonial Pipeline in 2021, which disrupted fuel supplies across the eastern United States.
  3. Security breaches at Nuclear Power Plants:
    • Description: Compromise of nuclear facilities can lead to unauthorized access to critical systems, potentially resulting in dangerous radiation releases.
    • Impact: Severe health and environmental risks, long-term contamination and loss of public confidence in nuclear safety.
    • Example: the Stuxnet worm, which targeted Iran’s nuclear facilities, highlighting vulnerabilities in nuclear security.
  4. Attacks on the Energy Supply Chain:
    • Description: Supply chain disruption can disrupt the delivery of essential resources such as fuel and equipment, paralyzing energy production and distribution.
    • Impact: Causes delays and shortages in energy supply, affecting all dependent sectors and potentially leading to cascading failures.
    • Examples: attacks on third-party suppliers and vendors, such as the SolarWinds hack, which demonstrated the potential for supply chain vulnerabilities to be exploited.

Mitigation Strategies:

  • Cybersecurity Incident Monitoring and Response : Implement advanced monitoring systems to detect and respond to threats in real time.
  • Security Audits and Penetration Tests: Conduct regular security audits and penetration tests to identify and address vulnerabilities.
  • Supply chain security: Enhance the security of supply chain operations through strict supplier verification and continuous monitoring.
  • Incident Response Planning: Develop and regularly update incident response plans to ensure rapid and effective responses to cyber incidents.
  • Collaboration and information sharing: Promote collaboration between industry stakeholders and government agencies to share threat intelligence and best practices.

By understanding these potential threats and implementing robust mitigation strategies, the energy sector can increase resilience against cyber-attacks and ensure the continued provision of essential services.


Conference report, May 2024.

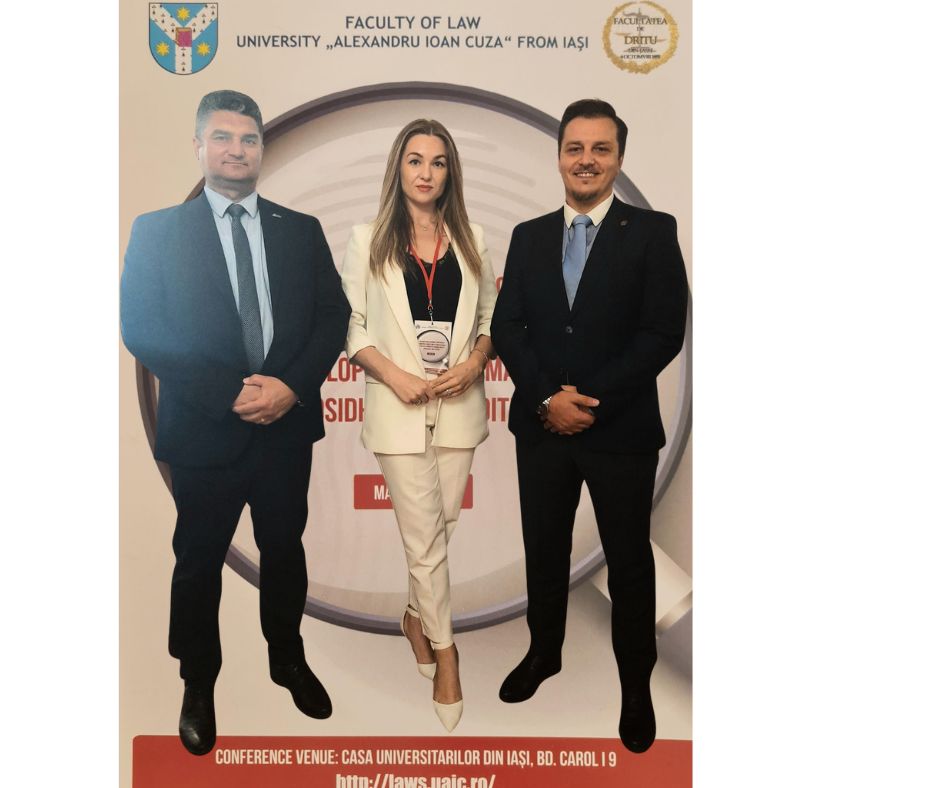
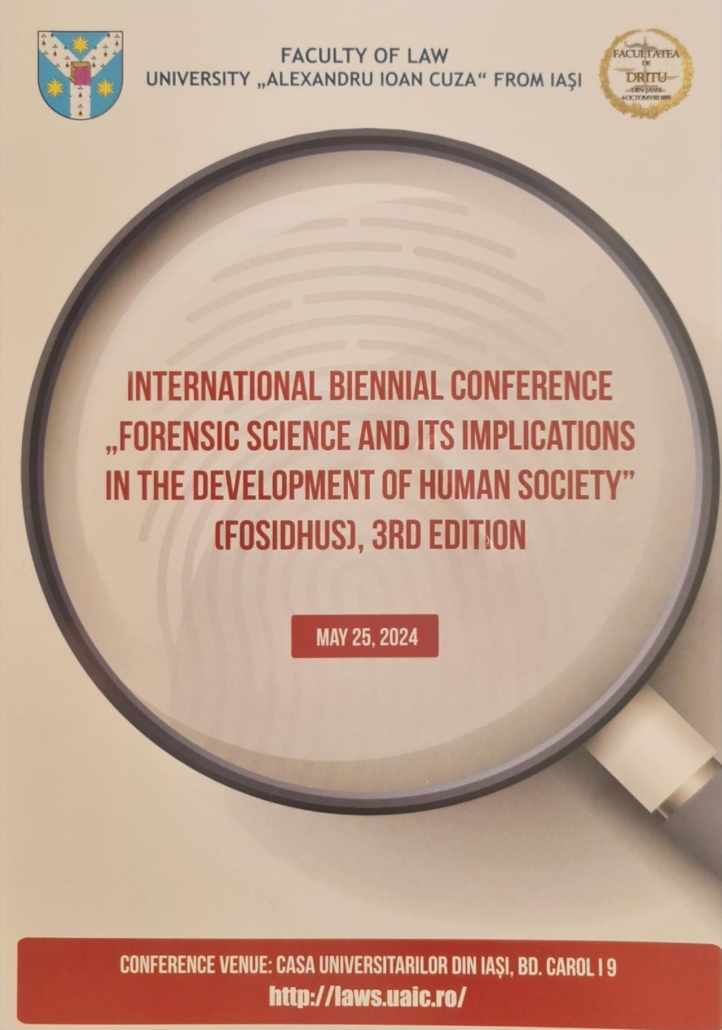
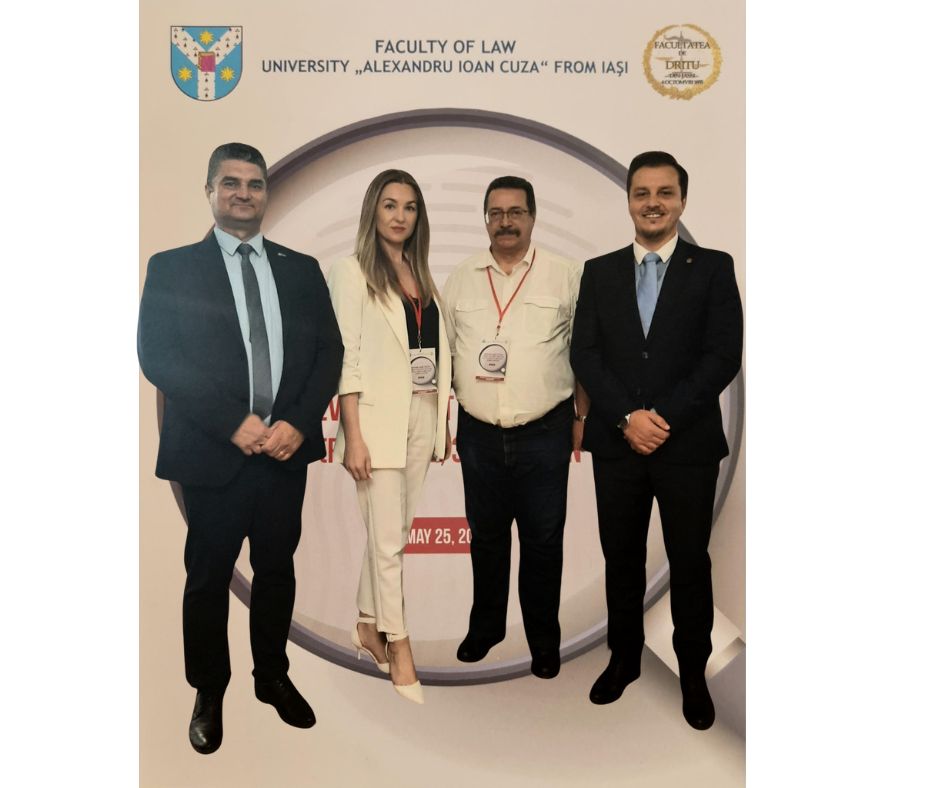
On 25 May 2024, ProDefence presented the paper “The criminal relevance of artifacts identified in cybercrime investigations” at the third edition of the international conference Forensic Science and its Implications in the Development of Human Society (FOSIDHUS), held at Casa Universitarilor in Iași and organised by the Faculty of Law of “Alexandru Ioan Cuza” University. The 2024 theme was “The challenges of forensic science in the digital age”.

Key points

  • Digital artifacts are traces left by users and programs: logs, browser history, registry entries, metadata, messages.
  • An artifact matters in a criminal case only if it can be linked to a person, an action and a moment in time.
  • The paper, co-presented with Florin Zaborilă, discussed how such traces are identified, interpreted and used in criminal proceedings.
  • Practitioners bring real cases and tools that complement academic research.

What the paper covered

Alexandru Angheluș and Florin Zaborilă discussed the importance of digital artifacts in criminal investigations and their impact on procedure. In practice, a single trace rarely proves anything on its own. Its value comes from:

  • integrity: showing that the trace was collected without being altered;
  • context: correlating it with other artifacts, such as timestamps, accounts and network data;
  • attribution: linking the activity to a specific device and, where possible, a specific person;
  • interpretation: explaining what the trace means in terms that lawyers and courts can assess.

Why practitioner contributions matter

Presentations by private-sector specialists at academic conferences such as FOSIDHUS add value in several ways:

  • Real-world experience: practitioners deal daily with new technologies and concrete cases, bridging theory and practice.
  • Techniques and tools: methods tested in real investigations reach the academic and professional community faster.
  • Collaboration: conferences connect the private sector with universities and public institutions.
  • Better practice and policy: field experience reveals gaps in current approaches and suggests improvements.
  • Professional development: participants learn current trends and build networks.
  • Research: new case studies open new research directions.

Acknowledgements

Special thanks to the organisers, especially Mrs. Ancuța Elena Frantz, and to the National Institute of Forensic Expertise, represented by Mr. Gabriel Dumitru Păduraru, for organisational support. Thanks to all participants for the discussions and exchange of ideas.

Related

ProDefence provides technical analysis in cybercrime cases and analysis of large case files and digital evidence. See also Cybercrime investigation in Romania.

Event report, May 2024.

Alexandru Angheluș, CEO of ProDefence, lectured at a cybersecurity session for prosecutors and police officers specialised in cybercrime investigation, together with Florin Ionuț Zaborilă. The session was part of the annual training programme organised by the Prosecutor’s Office attached to the Iași Court of Appeal and the General Inspectorate of the Romanian Police, Directorate of Criminal Investigations.

Key points

  • The lecture covered theoretical and practical aspects of cybersecurity and the methods used to compromise information systems.
  • Investigators need to understand attack techniques to know which traces to look for and where.
  • Public-private collaboration gives authorities access to technology, threat intelligence and specialised training.

The lecture

The presentation, “Theoretical and practical aspects of cybersecurity, methods of compromising information systems, useful information for authorities investigating cybercrime”, aimed to strengthen the technical investigation capabilities of law enforcement. Typical topics in such sessions include:

  • how attackers gain initial access: phishing, stolen credentials, vulnerable services;
  • how malware persists and communicates with its operators;
  • where traces remain on devices, servers and networks;
  • how to request and interpret data from service providers.

Why public-private collaboration matters

Cyber threats change quickly and investigations are complex. Collaboration between the public and private sectors brings concrete advantages:

  • Advanced technology: companies often have tools that help investigate and prevent cybercrime.
  • Information sharing: fast exchange of threat intelligence helps detect new tactics early.
  • Training: industry specialists help develop the technical skills of officers and prosecutors.
  • Additional resources: complex cases benefit from external technical capacity.
  • Adaptability: the private sector can respond quickly to new threats.
  • Better rules: ongoing dialogue leads to policies and laws better adapted to real needs.

Such collaboration strengthens the investigative capacity of authorities and creates a common front against cybercrime, protecting citizens and critical infrastructure.

Related

ProDefence offers cybercrime investigation support and cybersecurity training for institutions and companies. See also The criminal relevance of artifacts identified in cybercrime investigations.

Event report, 2024.

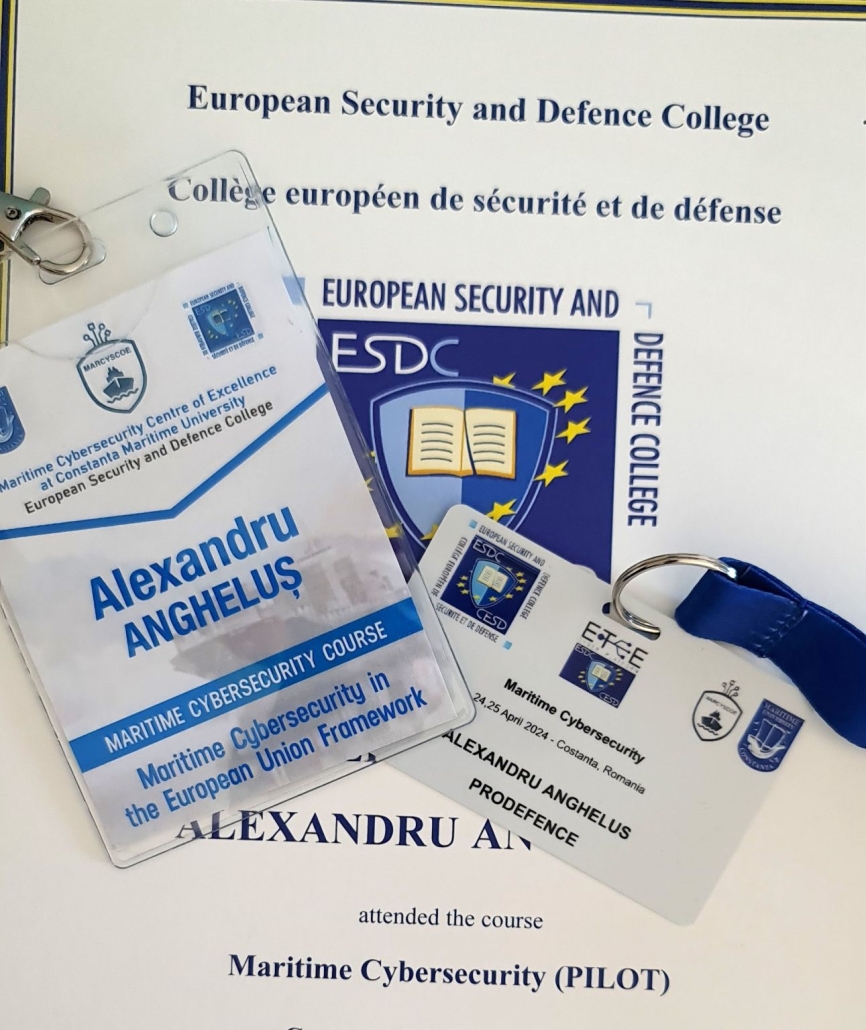
ProDefence took part in the Maritime Cybersecurity Course hosted by the Maritime Cybersecurity Centre of Excellence (MARCYSCOE) at Constanța Maritime University. The two-day programme was organised under the aegis of the European Security and Defence College (ESDC) and focused on protecting maritime operations against cyber threats.

Key points

  • Shipping and ports depend on interconnected systems: navigation, cargo management, port logistics, communications.
  • The course covered EU maritime cybersecurity policy, technical tools and strategies for identifying and managing threats.
  • Participants came from the public and private sectors, from Romania and other countries.
  • International and cross-sector cooperation is essential, since maritime incidents rarely stay within one jurisdiction.

Why maritime cybersecurity matters

Maritime operations rely more and more on digital technologies. A ransomware attack on a port operator, a compromised cargo management system or interference with navigation data can stop the movement of goods and affect entire supply chains. Ports and shipping companies are also covered by NIS2 in the transport sector, which adds legal obligations to the operational risk.

What the course covered

  • EU policy on maritime cybersecurity;
  • technological tools used to protect maritime systems;
  • strategies for identifying and managing cyber threats;
  • real case studies, interactive workshops and classes led by specialists.

Cooperation across borders and sectors

A highlight of the course was the interaction between participants from different countries and from both the public and private sectors. The exchange of ideas and practices supports stronger cross-border and cross-sector partnerships, which maritime security needs.

Thanks to the Maritime Cybersecurity Centre of Excellence for organising the programme.

Related

See the report from the BlackSea Maritime Cybersecurity Conference. For transport-sector organisations preparing for NIS2, ProDefence offers NIS2 compliance consulting and penetration testing.

Published in April 2024, after Master’s Week at the Faculty of Law of “Alexandru Ioan Cuza” University of Iași.

Online financial fraud is evolving fast: from crude phishing messages to fake investment platforms with paid ads, credible websites and “advisers” who call the victim. At Master’s Week, organised by the Law Students Association of Iași, ProDefence showed students part of the work of cybercrime investigators, with a focus on how legal and technical aspects fit together.

Key points

  • Fake investment schemes are among the most costly forms of online fraud.
  • The “Investor Fever” analysis shows step by step how these schemes work.
  • Future lawyers need to understand how a cybercrime investigation is carried out.
  • Collaboration between technical and legal specialists is essential in such cases.

What recent cases show

Talks on cybersecurity and cybercrime always raise curiosity: cases, investigations, victims, amounts and perpetrators. Trends seen in recent cases:

  • professionalised fraud: organised teams with distinct roles (marketing, “advisers”, money laundering);
  • apparent credibility: well-built websites, social media ads, fake reviews, sometimes the image of public figures;
  • psychological pressure: initial gains shown on the platform, then “fees” demanded for withdrawals;
  • repeat victimisation: the same groups return with “money recovery” offers.

A detailed case is described in Investor Fever: financial investment fraud, recommended to every internet user.

Why it matters for future lawyers

Spreading this information educates the public, but it is essential for those preparing for a legal career. Lawyers, judges and other legal professionals must be able to interpret and apply the law in cases with a digital component: to understand what an IP address is, what an access log shows or how funds moved into cryptocurrency are traced. Cybersecurity skills are also increasingly sought on the job market.

Legal and technical, together

A cybercrime case is built from technical evidence but decided in legal terms. Without a bridge between the two, valuable information is lost.

On the same occasion, the team of the General Anticorruption Directorate (DGA), Iași County Anticorruption Service, gave a presentation with very useful information.

Acknowledgements

Thanks to Chief Police Inspector Florin Ionuț Zaborilă, coordinator of the Cybercrime Investigation Department of the Iași County Police, for his ongoing collaboration and involvement in warning the public about online dangers. Thanks to the organisers and to “Alexandru Ioan Cuza” University of Iași for the invitation.

Have you been defrauded?

Contact your bank and report the case to the police immediately. For the technical documentation of the case, ProDefence offers analysis of electronic fraud and suspicious files and support in cybercrime cases.

Skip to content